Elsevier Science Publishing Co Inc
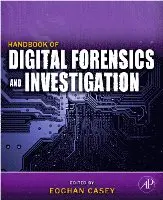
Handbook of Digital Forensics and Investigation
- Vikt 1,04 kg
499 krhos Akademibokhandeln · exkl. frakt
9 kr skillnad mellan billigaste och dyraste butik i lager
Dubbelkollade priser
Jämför 3 butiker
- Akademibokhandeln, 499 kr, frakt enligt butiken. Till butik (öppnas i ny flik)
I lagerFrakt: se butikenDubbelkollad 11:18
499 kr
Lägst
- Bokus, 508 kr, frakt enligt butiken. Till butik (öppnas i ny flik)
I lagerFrakt: se butikenDubbelkollad 10:51
508 kr
- Adlibris, 514 kr, frakt enligt butiken. Till butik (öppnas i ny flik)
Slut i lagerFrakt: se butikenDubbelkollad 27 okt. 09:10
514 kr
Priser från butikernas flöden kan ha ändrats: det är priset hos butiken som gäller, så kontrollera det innan du handlar.
Prishistorik
Köp nu eller vänta?
Just nu kostar produkten 499 kr — 6 kr över det lägsta vi sett på 1 månad.
Pris idag
499 kr
- Lägst
- 493 kr
- Snitt
- 496 kr
- Högst
- 499 kr
| 2026-09-15 | 493 kr · Lägst hos Bokus |
|---|---|
| 2026-10-11 | 499 kr · Lägst hos Akademibokhandeln |
Om produkten
Handbook of Digital Forensics and Investigation
Läs merLäs mindre
Handbook of Digital Forensics and Investigation builds on the success of the Handbook of Computer Crime Investigation, bringing together renowned experts in all areas of digital forensics and investigation to provide the consummate resource for practitioners in the field. It is also designed as an accompanying text to Digital Evidence and Computer Crime. This unique collection details how to conduct digital investigations in both criminal and civil contexts, and how to locate and utilize digital evidence on computers, networks, and embedded systems. Specifically, the Investigative Methodology section of the Handbook provides expert guidance in the three main areas of practice: Forensic Analysis, Electronic Discovery, and Intrusion Investigation. The Technology section is extended and updated to reflect the state of the art in each area of specialization. The main areas of focus in the Technology section are forensic analysis of Windows, Unix, Macintosh, and embedded systems (including cellular telephones and other mobile devices), and investigations involving networks (including enterprise environments and mobile telecommunications technology). This handbook is an essential technical reference and on-the-job guide that IT professionals, forensic practitioners, law enforcement, and attorneys will rely on when confronted with computer related crime and digital evidence of any kind.Provides methodologies proven in practice for conducting digital investigations of all kindsDemonstrates how to locate and interpret a wide variety of digital evidence, and how it can be useful in investigationsPresents tools in the context of the investigative process, including EnCase, FTK, ProDiscover, foremost, XACT, Network Miner, Splunk, flow-tools, and many other specialized utilities and analysis platformsCase examples in every chapter give readers a practical understanding of the technical, logistical, and legal challenges that arise in real investigations
Specifikationer
Fakta
- Vikt
- 1,04 kg
- GTIN
- 09780123742674
Uppgifter från tillverkare och butiker.