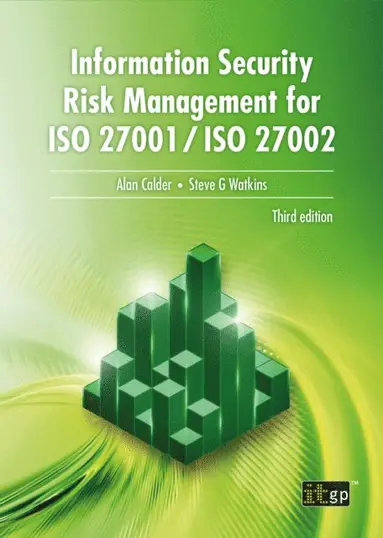
Information Security Risk Management for ISO 27001/ISO 27002
Dubbelkollade priser
Jämför 2 butiker
- Bokus, 466 kr, frakt enligt butiken. Till butik (öppnas i ny flik)
I lagerFrakt: se butikenDubbelkollad 02:51
466 kr
Lägst
- Adlibris, 466 kr, frakt enligt butiken. Till butik (öppnas i ny flik)
Slut i lagerFrakt: se butikenDubbelkollad 27 okt. 09:10
466 kr

Priser från butikernas flöden kan ha ändrats: det är priset hos butiken som gäller, så kontrollera det innan du handlar.
Prishistorik
Köp nu eller vänta?
Just nu kostar produkten 466 kr — 35 kr över det lägsta vi sett på 1 månad.
Under den tiden har det oftast legat runt 440–470 kr.
Pris idag
466 kr
- Lägst
- 431 kr
- Snitt
- 458 kr
- Högst
- 466 kr
| 2026-09-15 | 461 kr · Lägst hos Bokus |
|---|---|
| 2026-09-18 | 431 kr · Lägst hos Bokus |
| 2026-09-20 | 466 kr · Lägst hos Bokus |
| 2026-09-24 | 431 kr · Lägst hos Bokus |
| 2026-09-27 | 466 kr · Lägst hos Bokus |
| 2026-10-13 | 440 kr · Lägst hos Bokus |
| 2026-10-21 | 466 kr · Lägst hos Bokus |
Om produkten
Information Security Risk Management for ISO 27001/ISO 27002
Läs merLäs mindre
Protect your information assets with effective risk managementIn today's information economy, the development, exploitation and protection of information and associated assets are key to the long-term competitiveness and survival of corporations and entire economies. The protection of information and associated assets - information security - is therefore overtaking physical asset protection as a fundamental corporate governance responsibility. Information security management system requirementsISO 27000, which provides an overview for the family of international standards for information security, states that "An organisation needs to undertake the following steps in establishing, monitoring, maintaining and improving its ISMS [...] assess information security risks and treat information security risks". The requirements for an ISMS are specified in ISO 27001. Under this standard, a risk assessment must be carried out to inform the selection of security controls, making risk assessment the core competence of information security management and a critical corporate discipline.Plan and carry out a risk assessment to protect your informationInformation Security Risk Management for ISO 27001 / ISO 27002:Provides information security and risk management teams with detailed, practical guidance on how to develop and implement a risk assessment in line with the requirements of ISO 27001.Draws on national and international best practice around risk assessment, including BS 7799-3:2017 (BS 7799-3).Covers key topics such as risk assessment methodologies, risk management objectives, information security policy and scoping, threats and vulnerabilities, risk treatment and selection of controls.Includes advice on choosing risk assessment software.Ideal for risk managers, information security managers, lead implementers, compliance managers and consultants, as well as providing useful background material for auditors, this book will enable readers to develop an ISO 27001-compliant risk assessment framework for their organisation and deliver real, bottom-line business benefits.Buy your copy today!About the authorsAlan Calder is the Group CEO of GRC International Group plc, the AIM-listed company that owns IT Governance Ltd. Alan is an acknowledged international cyber security guru and a leading author on information security and IT governance issues. He has been involved in the development of a wide range of information security management training courses that have been accredited by IBITGQ (International Board for IT Governance Qualifications). Alan has consulted for clients in the UK and abroad, and is a regular media commentator and speaker. Steve Watkins is an executive director at GRC International Group plc. He is a contracted technical assessor for UKAS - advising on its assessments of certification bodies offering ISMS/ISO 27001 and ITSMS/ISO 20000-1 accredited certification. He is a member of ISO/IEC JTC 1/SC 27, the international t