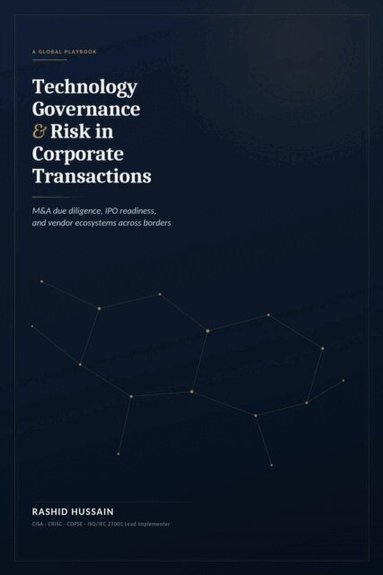
Technology Governance & Risk in Corporate Transactions
Dubbelkollat idag
Jämför 1 butik
- Bokus, 120 kr, frakt enligt butiken. Till butik (öppnas i ny flik)
I lagerFrakt: se butikenDubbelkollad 11:51
120 kr
Lägst
Priser från butikernas flöden kan ha ändrats: det är priset hos butiken som gäller, så kontrollera det innan du handlar.
Om produkten
Technology risk has moved from the server room to the boardroom
Läs merLäs mindre
A ransomware attack can halt production lines within hours. A misconfigured cloud bucket can expose millions of records overnight. A vendor's unpatched vulnerability can become the acquirer's liability the moment a deal closes. Yet most corporate transactions still treat technology and cybersecurity due diligence as a checkbox exercise - delegated to an IT consultant, read by no one outside the technical team, and disconnected from the legal and financial mechanics that actually protect deal value.Technology Governance & Risk in Corporate Transactions closes that gap. Written by a legal and technology governance professional with over fifteen years of senior in-house experience - including direct involvement in a private equity acquisition and an active IPO process - this book is a practitioner's playbook for managing technology risk across the full lifecycle of a corporate transaction.Across seventeen chapters, the book covers:- Technology and cybersecurity due diligence in M&A, from pre-signing investigation through post-merger integration- Data privacy diligence across GDPR, Saudi Arabia's PDPL, US state law, and China's PIPL- Cyber risk quantification and deal pricing, including risk-adjusted valuation bridges- IPO and listing readiness, including board oversight, audit-ready ISMS structures, and case study themes drawn from an ISP and technology-sector listing journey- Global vendor and third-party risk management, cloud and outsourcing contracts, and fourth-party supply chain exposure- Cross-border data transfer compliance and emerging regulation, including the EU AI Act and DORA- A repeatable governance framework, complete with diligence checklists, a vendor risk tiering template, a maturity model, and a references appendixWritten with a deliberately global perspective and grounded in frameworks including ISO/IEC 27001, NIST CSF, and COBIT, this book is essential reading for legal counsel, risk officers, CISOs, board members, and deal advisors working on transactions that cross borders and regulatory regimes.